Responsible AI Advisory · Speaking · Training · Diagnostics

“Who approved this?”

It's the question every board eventually asks about AI, usually after something has already gone quietly wrong. Kivè Advisory helps executive teams answer it before it's asked, through keynotes, executive training and rapid diagnostics drawn from 20 years of IT risk and audit work.

From the field
"No system broke. No model malfunctioned. The real failure was structural — and it's already happening inside your organisation."
— from the forthcoming book, Responsible AI: An Executive Perspective
Why now

AI is already inside your organisation

Employees are already using AI tools that leadership has never approved, so decisions are being made with AI that no one in the organisation has reviewed or signed off.

  • 86% of global executives now rate technology risk as high impactKiteworks, 2026
  • 53% of organisations report feeling overwhelmed by AI-specific regulationsVanta, 2026
  • 71% of UK employees have used unapproved consumer AI tools at workMicrosoft, 2025
  • 83% of organisations plan to deploy agentic AI into their business functions, but only 31% feel fully equipped to secure those systemsCisco, 2025
How we help

Three ways to work together

All three draw on the same framework and experience, shaped for the audience in front of you: a board, a leadership team or a conference hall.

Speaking

Keynotes & Speaking

A talk built around one AI incident: what happened, who should have caught it, and why AI governance belongs with the executive team.

  • Board offsites & leadership summits
  • Conference & industry keynotes
  • 45–60 minute talk, tailored to sector
Training

Executive Masterclass

The three-module programme behind Gloria's forthcoming book, Responsible AI: An Executive Perspective, delivered live to your CIO, CDO and their leadership teams.

  • The Wake-Up Call: the AI incident that no one saw coming
  • The Redefined Mandate: the new CIO / CDO role
  • The Real Risks: a working governance framework
Diagnostic

Rapid AI Diagnostic

A fixed-scope engagement that maps your organisation's AI risk exposure, including the cyber security risk that AI adds, against the four stages of the framework: Identify, Categorise, Prioritise, Operationalise.

  • Structured interviews across IT, data, risk & legal
  • Amplified cyber security exposure, mapped and prioritised
  • A prioritised, board-ready risk map
  • Typically 2–4 weeks, fixed scope
How we work

The framework behind every engagement

Without a shared framework, AI risk controls become fragmented, effort is duplicated and nobody is clearly accountable. Every engagement follows the same four stages.

i.

Identify

Map risk across data, model behaviour, access, and decision impact using a common taxonomy.

ii.

Categorise

Treat AI risk as something that magnifies the IT risks you already manage, and classify it within the risk domains you already use.

iii.

Prioritise

Allocate attention to the risks with the greatest operational and reputational exposure.

iv.

Operationalise

Embed controls into daily execution with clear ownership, documentation, and escalation.

Score your organisation against the four stages

“Artificial intelligence is the biggest commercial opportunity for companies, industries, and nations over the next few decades.”

— PwC Report

“By far the greatest danger of Artificial Intelligence is that people conclude too early that they understand it.”

— Eliezer Yudkowsky, Global Catastrophic Risks (2008)
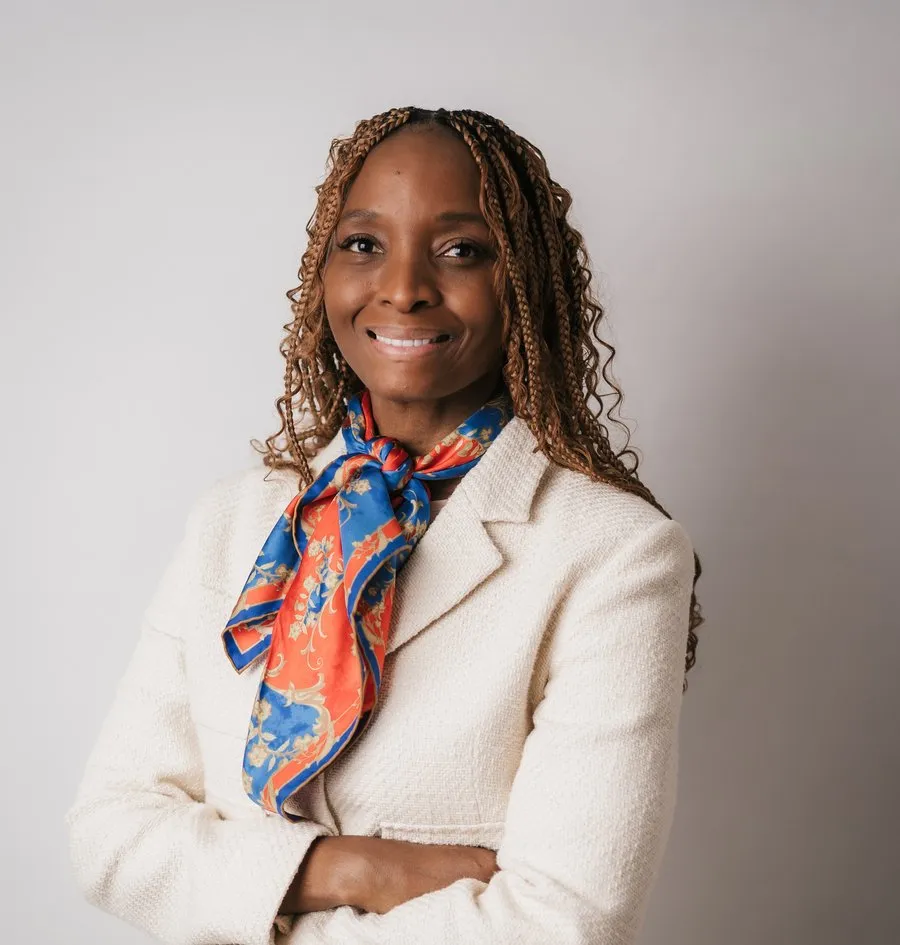
Gloria Croxall, Founder, Kivè Advisory
About Gloria Croxall

20 years in professional services, 10 of them in the Big Four

Gloria Croxall is the founder of Kivè Advisory and author of the forthcoming book Responsible AI: An Executive Perspective, out later this year. Across 20 years in professional services, including 10 at PwC, Deloitte and KPMG and ERP programme work at Accenture, she has led IT SOx, ITGC, cyber audit and technology risk engagements for global organisations, work that took her from London to Salt Lake City, Singapore to Johannesburg.

She brings that background, from large-scale SOx transformations and third-party risk assurance to GRC advisory across financial services, TMT, energy and logistics, to every keynote, masterclass and diagnostic.

  • 20 years professional services, incl. 10 in the Big Four
  • CISA, CRISC & ISO 27001 Lead Auditor certified
  • Global advisory: UK, US, Singapore & South Africa
  • Forthcoming author, Responsible AI: An Executive Perspective
  • ERP programme experience (SAP, GRC) from Accenture
20+
years in IT risk & controls advisory
4
Big Four & global firms: PwC, Deloitte, KPMG, Accenture
4
regions served: UK, Europe, US & APAC
FS · TMT · Energy · Logistics
sectors advised, alongside retail & public sector
Let's talk

Book a conversation

Tell us about the keynote, masterclass or diagnostic you have in mind, and we'll reply within two business days.

hello@kiveadvisory.com

We'll reply within 2 business days.
Thanks, your request has been sent. We'll reply to the email address you gave within two business days.